Blog

Tweet

Interrogation with Apport hooks - Qt Included

Earlier today my buddy Martin Pitt blogged about how he needed a Qt developer to work on implementing theui_question_choice() dialog. I looked through the code a bit this morning, and needed a little help right off the bat getting the GTK version running. One little thing I missed a bug report and Martin helped get it up and running. So as the day went on, storms came through, and for some reason I get in this storm hunter mode and nothing else gets done. Well, about an hour ago all the storms have cleared up and back to work I went. I spent about an hour, most of which was silly Qt Designer and layouts, which Kubuntu guys, I suck at, never listen to me brag about my Qt Designer classes again! The other thing that had me for a second was trying to iterate over a layout to get button statuses. After all was said and done, this is the little beauty that popped up when testing:
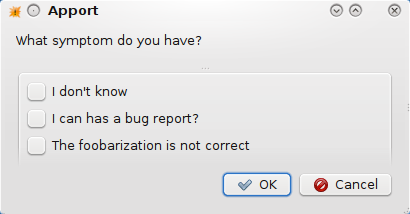
apport-qt4

Not to shabby. I will spend some time looking through all of the apport-qt ui stuff and see if I can make it as simple as the GTK side. The checkboxes in that image are generated dynamically by the hook. So once they are added to the layout, trying to figure out their status when they weren’t provided a name was tricky. Thankfully the PyQt 4 API Documentation is great!

So here it is, there is the main dialog and then there is the groupbox with a vertical box inside of it. The vertical box makes it simple to add and remove stuff so that’s why I went that route, KISS. So after the box is populate, you select the stuff you need then press OK to submit it. Well the trick was finding out what is checked. So the main dialog is nameddialog and the vertical box that holds the check boxes is calledvbox_choices. So here is how I got those values:

result = []
for c in range(0, dialog.vbox_choices.count()):
    if dialog.vbox_choices.itemAt(c).widget().isChecked():
        result.append(c)

So, the main reason for doing this, is so I can find it a bit easier next time, and the fact that I couldn’t find this little bit documented anywhere else. If there is a better way to do this, let me know.

EDIT: Removed theindex variable as it was old code left hanging around when I did the copy and paste. Thanks Milian for catching that.

Posted in Application, Development, Linux | Tagged , , , , | 12 Comments
Tweet

GPG Transitioning

Yay, I am doing the transitioning too. So w/o further ado, welcome my new GPG key:

pub   4096R/D8C44738 2009-06-06
      Key fingerprint = 3578 0981 A21D D662 2A96  7623 F4C1 838C D8C4 4738
uid                  Richard A. Johnson <[email protected]>
uid                  [jpeg image of size 12182]
sub   4096R/6B8A7765 2009-06-06

Yes, I even added my picture to the key, because it is even groovier that way.

And now say goodbye to my old key (well not yet, transitioning it out, so use the new key instead from now on):

pub   1024D/2E2C0124 2006-05-21
      Key fingerprint = 9554 2BCC 3AA2 3898 0939  56E7 3EC9 A39D 2E2C 0124
uid                  Richard A. Johnson <[email protected]>
sub   2048g/B9DDBD35 2006-05-21

So, if you have signed my key in the past, I wrote up one of those transitioning letters that are signed by both keys. You can download that HERE. You can also DOWNLOAD the public key if you really need it, or you can just do the following to get it:

gpg --keyserver keyserver.ubuntu.com --recv-key D8C44738

So if you feel safe enough, without having to go through my wallet to verify I do in fact own the new key, I would appreciate it if you would sign it, if not I understand, and the next time we are face-to-face, you are buying beer! :)

Posted in Personal | Tagged | 2 Comments
Tweet

Apt URL Part Two

OK, so after going through comments on my previous post about Apt URL it has become obvious to me. Apt URL is a band aid more than it is a way for people to easily distribute software. Is this a bad thing? No, not in my personal opinion. It seems the main arguments I received in the post, and especially on IRC (thanks to all of you who messaged me bitching me out, that rocks!) as as follows:

  1. Once Ubuntu is released, we aren’t getting new updates.
  2. Package so-and-so hasn’t been updated in 2 years
  3. This will allow software developers to get their software out to more people.

OK, so it is obvious why I call Apt URL a band aid, and points #1 and #2 show this. For point #1 it is obvious that Backports aren’t getting utilized as they probably should. Point #2 shows us that there are more merges on MoM than there are developers to handle that, and that there is a ton of software we aren’t paying attention to. This is something that has to be fixed, but has proven difficult for the past few years.

That brings me to point #3. In a comment in my last post, Skype was brought up, and how it isn’t in the Ubuntu repositories. Is there a reason that Skype can’t go into Multiverse or the Canonical repositories? Is there something I am missing when it comes to the non-free repositories? I will admit I do not follow them since I attempt to keep my system RMS happy :p

OK, so here is my other question, slash, problem. Security! I keep hearing about this “whitelist.” Am I to expect that people are going to go through the Core Developer process in order to get on this so-called whitelist? If you don’t do a process like this, well you just flat out disrespected every MOTU and Core Developer in our community. If you make them go through a process like this, then why can’t they be a MOTU or Core Developer in Ubuntu? This is my big issue really. If you don’t make them go through the process that every MOTU and Core Developer has done then you might as well spit in those people’s faces who have put their blood, sweat, and tears into gaining a certain level of trust. And if you do make them go through the same process, then what the heck, it makes no sense.

I am still looking for solid information on why this is good, and how it can be utilized for something other than a band aid. Martin Owens had my favorite comment on the previous post, about what kind of society do I think we live in and what not. Martin, we live in a society right now where people need protection more than anything. I am not talking about the old G-Dub terrorist protection plan, I am talking about those evil little kids in mommy and daddy’s basement using other people’s scripts to do damage. Linux, just like Windows and Mac, is as secure as its user. I think it is in Ubuntu’s best interest to protect the users as much as possible, but not to the point where we cut off their freedoms. If people want Apt URL, give it to them, but I think Ubuntu should make the same statement it did about Automatix years back.

If we want to make it easy for people to get the latest and greatest software, then we need to start working on fixing our infrastructure so we can do it correctly and safely. Since there is no single package manager to rule them all, Linux software distribution will continue to be a pain in the ass. Here is an idea. How about a mailing list or such, where upstream developers can announce new software, updated software, and what not? Everyone who wants to be a packager, look there and get to work? There has to be a way to have solid upstream <—> downstream communications, it is sounding like it isn’t happening to me.

Posted in Application, Linux | Tagged | 14 Comments
  • Subscribe to nixternal.com

     Subscribe in a reader

    Or, subscribe via email:
    Enter your email address:

  • Archives

semidetached
semidetached
semidetached
semidetached